The U.S. Department of Health and Human Services (HHS), Office for Civil Rights (OCR) has the authority to investigate complaints and conduct compliance reviews involving potential violations of the HIPAA Privacy, Security, and Breach Notification Rules by covered entities and business associates.
Deer Oaks – The Behavioral Health Solution, an Affiliated Covered Entity under 45 C.F.R. §§ 160.103 and 164.105, is subject to these HIPAA requirements.
Background
On December 6, 2021, HHS received a complaint alleging that Deer Oaks Geriatric Services PC, doing business as Deer Oaks Consultation Services (DOCS), impermissibly disclosed protected health information (PHI) by making patient discharge forms publicly accessible online. These forms contained sensitive data including patient names, dates of birth, identification numbers, facilities, and diagnoses. The exposed PHI was finally secured in May 2023.
Further, on August 29, 2023, Deer Oaks experienced a cybersecurity breach when a threat actor exploited a network vulnerability, exfiltrated patient data, and demanded ransom to prevent publication of the PHI on the dark web.
OCR Findings
Following its investigation, OCR determined that Deer Oaks engaged in the following conduct:
- Impermissible disclosure of PHI not required or permitted under the HIPAA Privacy Rule (45 C.F.R. § 164.502(a)).
- Failure to perform an accurate and thorough risk analysis to identify potential risks and vulnerabilities to the confidentiality, integrity, and availability of electronic PHI, as required by the HIPAA Security Rule (45 C.F.R. § 164.308(a)(1)(ii)(A)).
Settlement Terms
To resolve these findings, Deer Oaks agreed to:
- Pay $225,000 to HHS in a single lump-sum payment.
- Enter into a Corrective Action Plan (CAP) monitored by OCR.
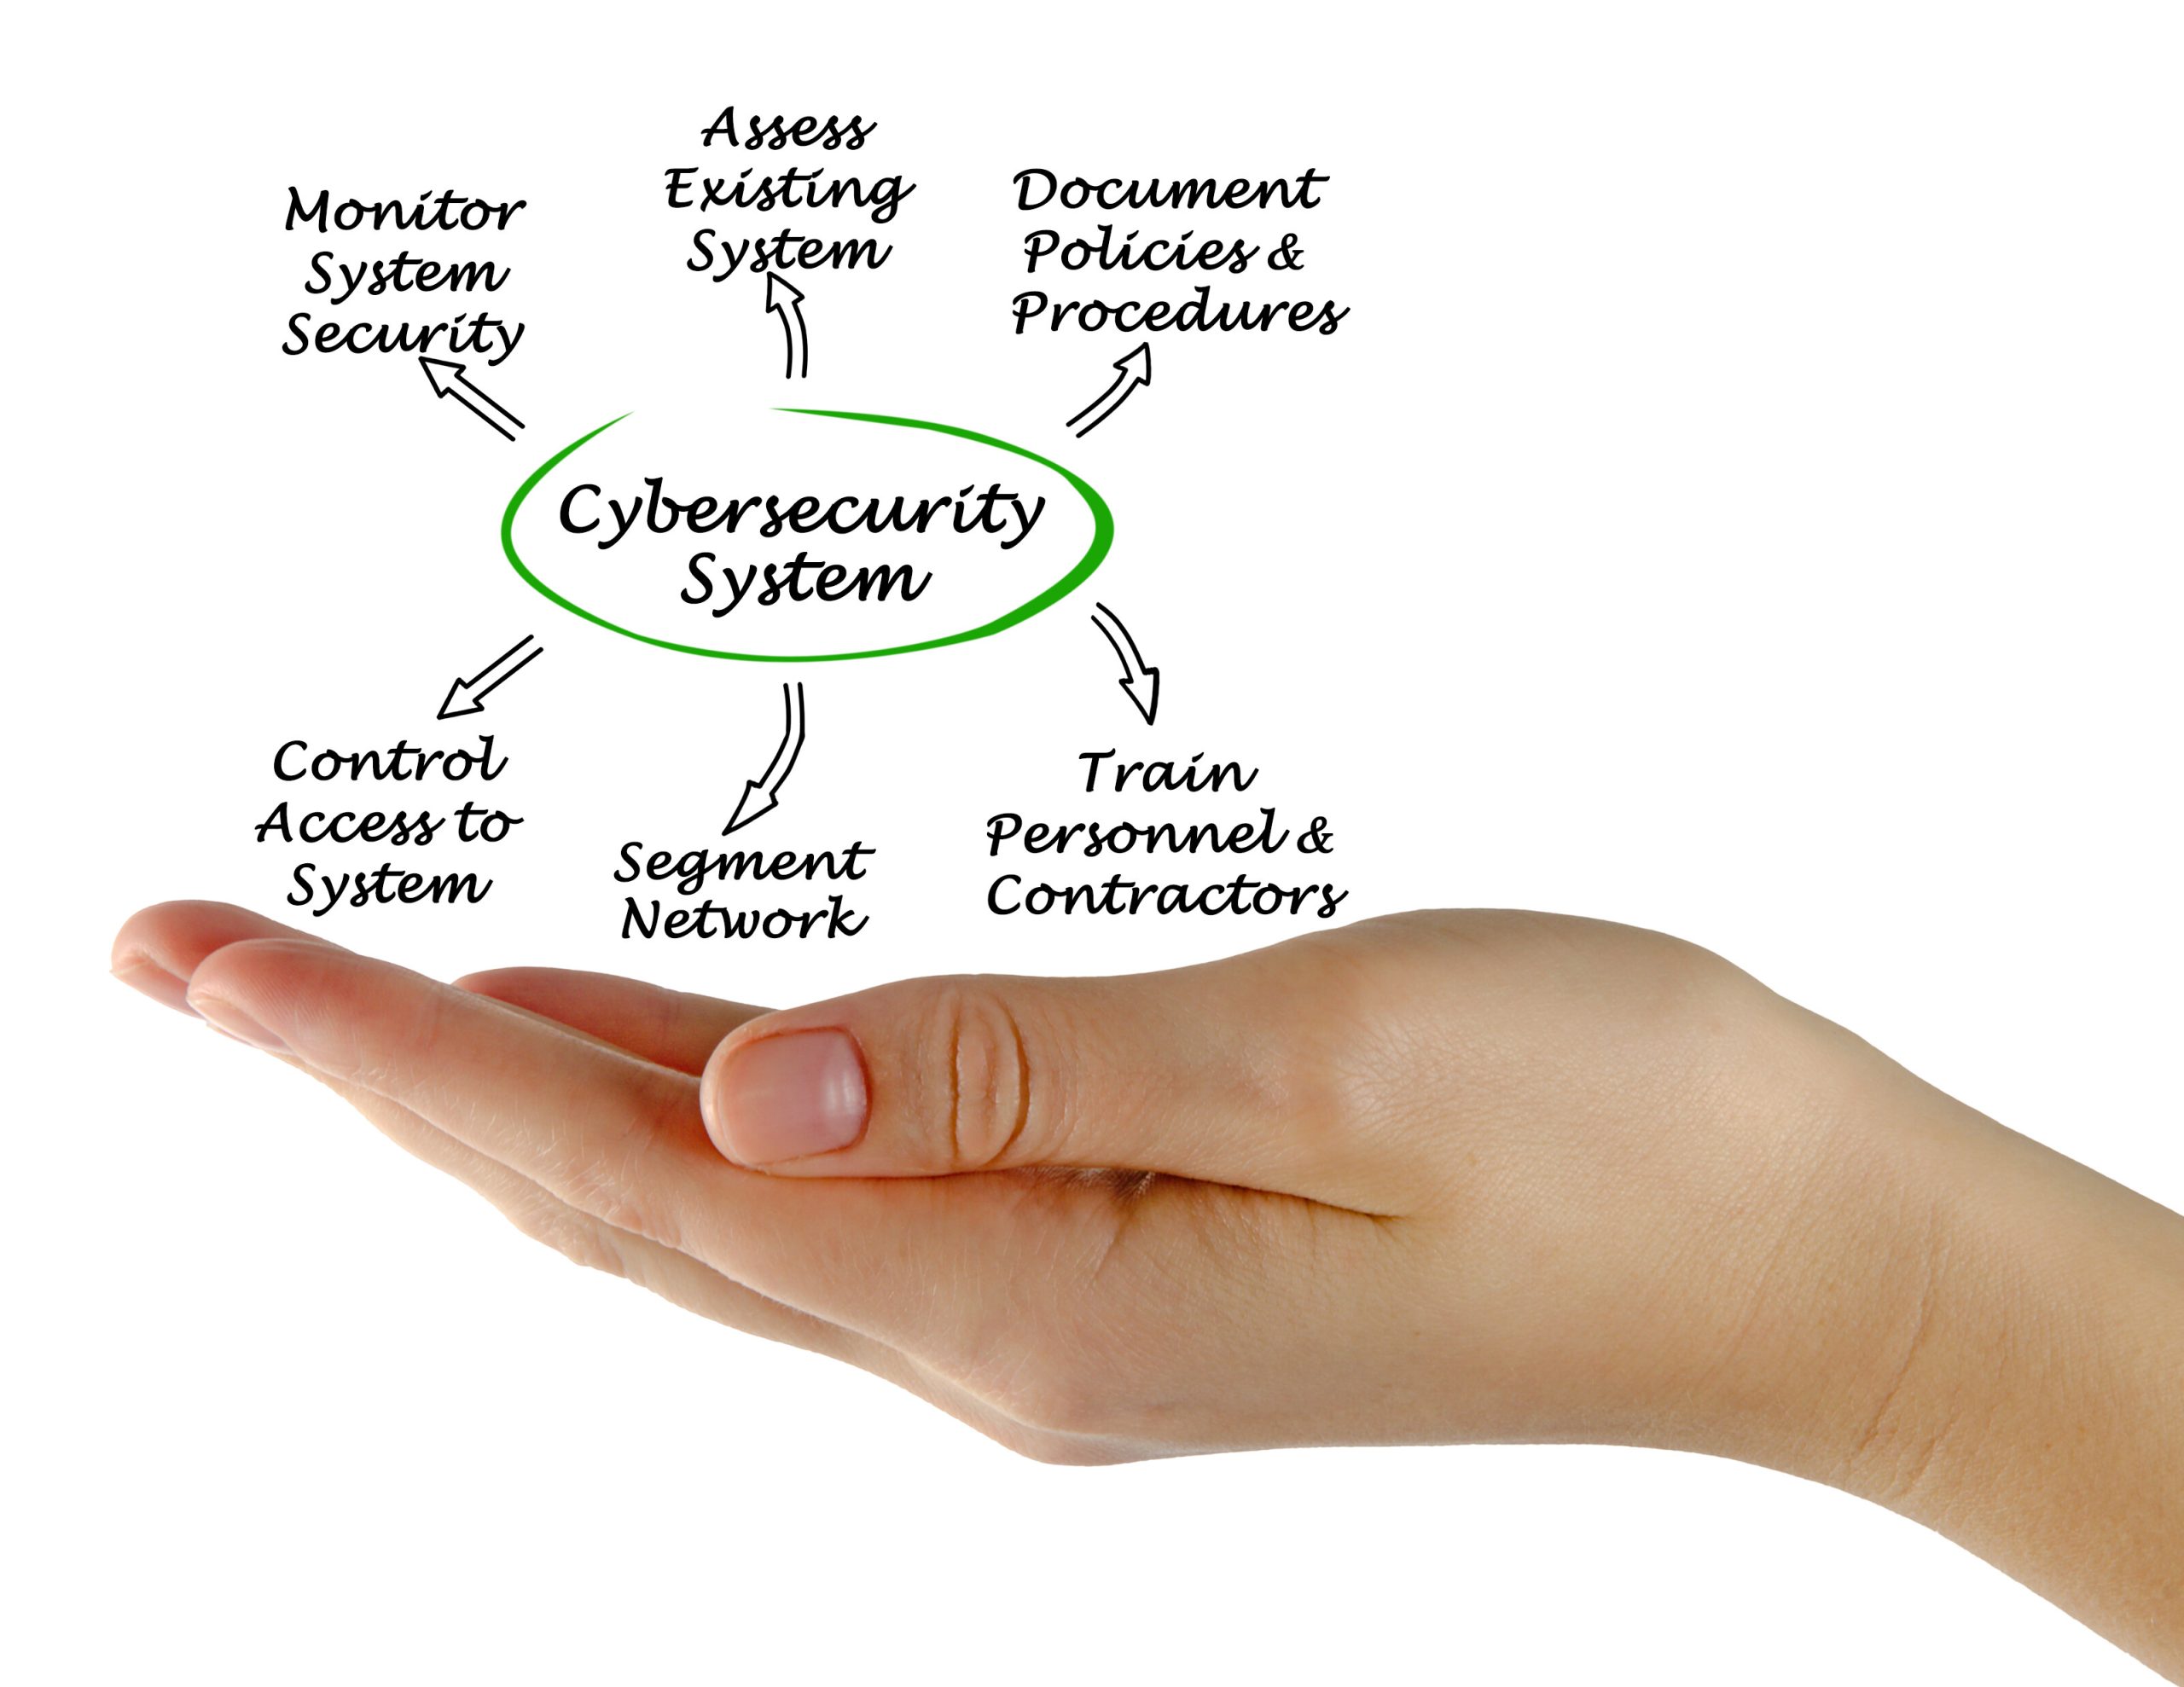
Under the CAP, Deer Oaks must implement a comprehensive HIPAA compliance program, including a full risk analysis, risk management plan, and updated policies, procedures, and workforce training to prevent future violations.
OCR clarified that this resolution does not release Deer Oaks from any future enforcement actions unrelated to the covered conduct or from potential criminal liability under 42 U.S.C. § 1320d-6.
Key Takeaway
This case is another reminder that HIPAA compliance goes far beyond securing data – it requires knowing where your data resides and who has access to it.
Without a system-wide risk analysis to map data flow and identify vulnerabilities, covered entities and business associates leave themselves open to both cyberattacks and regulatory penalties.
At Aris Medical Solutions, our HIPAA Keeper™ platform helps healthcare organizations perform a complete risk analysis, implement risk management strategies, and maintain ongoing compliance with the HIPAA Privacy and Security Rules—all within one secure, cloud-based system.
Don’t wait for an OCR complaint to expose your weaknesses, schedule your annual HIPAA Risk Analysis today.